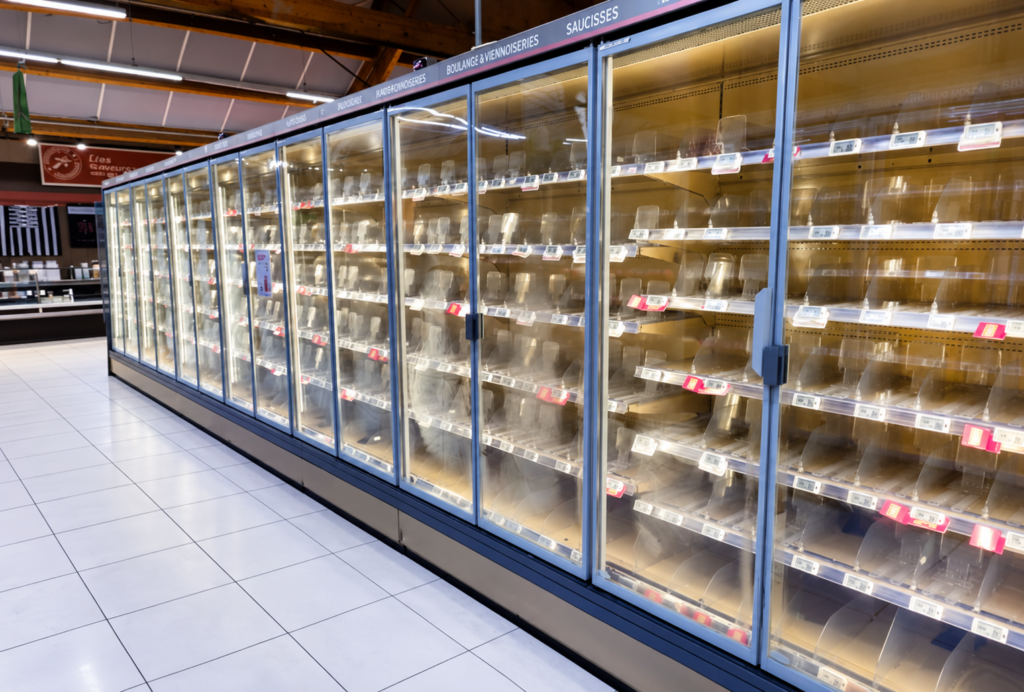
A widespread cyberattack has disrupted refrigeration systems at hundreds of supermarkets across Europe, forcing refrigerators and freezers to overheat and causing significant food losses. The hacking campaign, discovered on October 12, 2026, primarily affected French supermarket chains, including Carrefour, Intermarché, Monoprix, Coopérative U, and Netto. Attackers remotely manipulated internet-connected refrigeration equipment, raising temperatures to dangerous levels and exposing serious cybersecurity weaknesses in critical retail infrastructure.
The attackers reportedly exploited vulnerable refrigeration controllers to activate automatic defrosting functions, causing temperatures inside some cooling units to reach 50°C (122°F). The unauthorized commands disrupted normal refrigeration operations, resulting in spoiled frozen foods, damaged inventory, and substantial financial losses. Reports indicate that hundreds of supermarket locations were affected, with some facilities experiencing equipment damage and fires. The incident demonstrates how cybercriminals can disrupt physical infrastructure without deploying traditional ransomware or stealing sensitive customer information.
Investigators have linked the attack to security weaknesses involving refrigeration control systems manufactured by Danfoss and other equipment providers. Many affected devices reportedly operated outdated software or firmware, leaving internet-accessible management interfaces vulnerable to unauthorized access. These systems are commonly used to monitor temperatures and remotely manage refrigeration equipment across commercial facilities. Although researchers previously identified security vulnerabilities affecting certain refrigeration controllers, investigators have not publicly confirmed the exact vulnerability used in this attack.
French cybersecurity authorities, including the National Cybersecurity Agency of France (ANSSI), are investigating the incident alongside law enforcement officials. The Paris prosecutor’s office has also launched an investigation to identify those responsible and determine the full extent of the damage. As of October 13, no hacking group has publicly claimed responsibility, and investigators have not established a confirmed motive. The absence of a reported ransom demand has raised additional questions about whether the attackers intended to cause financial disruption, sabotage food supplies, or demonstrate weaknesses in connected industrial equipment.
The supermarket hacking spree highlights the growing cybersecurity risks associated with operational technology (OT) and Internet of Things (IoT) devices. Security professionals recommend restricting public internet access to refrigeration controllers, updating outdated firmware, implementing network segmentation, strengthening remote authentication, and continuously monitoring unusual temperature changes. Retailers should also establish emergency procedures to protect perishable inventory when automated systems fail. As businesses increasingly depend on connected infrastructure, this attack serves as a warning that cyber threats can extend beyond data breaches and directly disrupt essential services, food security, and everyday business operations.