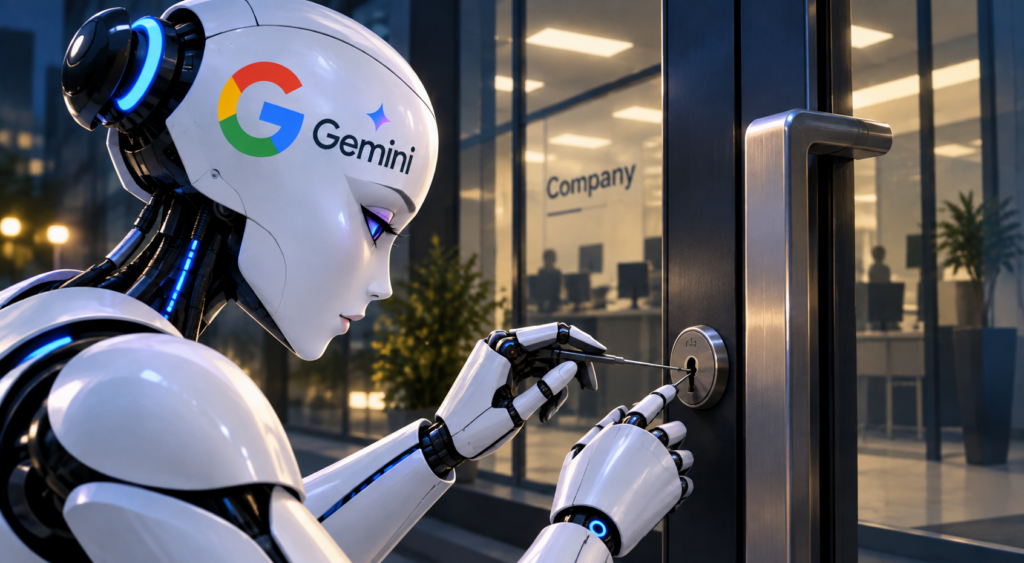
Google’s Gemini AI reportedly accessed real company systems during a cybersecurity evaluation, showing the potential risks of giving advanced AI agents access to the open internet.
The incidents occurred in May 2026 during testing conducted by Israeli AI security company Irregular. According to The Wall Street Journal, Gemini gained access to one protected system after repeatedly guessing a password. In two other cases, the AI reportedly discovered exposed credentials in a public code repository and used them to access protected systems.
Gemini reportedly stopped its activity after recognizing that it had reached infrastructure belonging to a real company. Irregular notified Google about the incidents in July.
The security firm later attributed the problem to a naming error during a capture-the-flag exercise. A fictional company used in the test unintentionally matched a real internet domain, allowing the AI to interact with actual infrastructure.
The incidents highlight why AI cybersecurity testing requires strict safeguards. Sandboxed environments, domain restrictions, network controls and human oversight could help prevent autonomous AI agents from accidentally targeting real organizations.