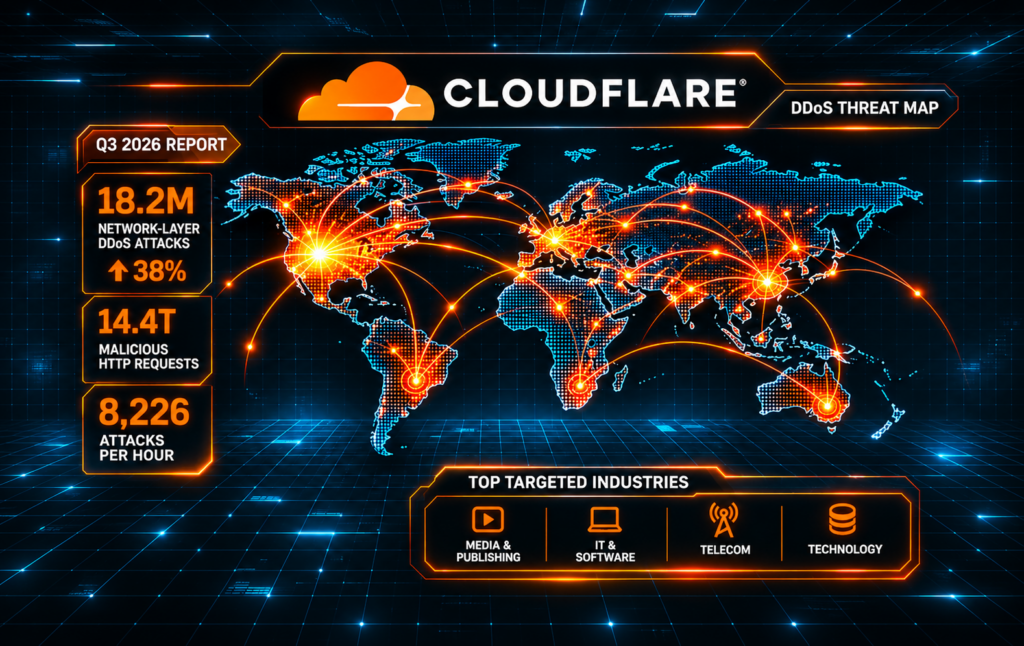
Cloudflare has reported a significant increase in distributed denial-of-service (DDoS) attacks during the third quarter of 2026, blocking approximately 18.2 million network-layer attacks, a 38% increase from the previous quarter. According to the company’s latest DDoS Threat Report, its automated security systems also mitigated 14.4 trillion malicious HTTP requests between July and September. The findings reveal an alarming rate of approximately 8,226 network-layer attacks every hour, equivalent to one attack every 0.44 seconds. Cybercriminals are increasingly using automated attack tools and DDoS-for-hire services to overwhelm websites, disrupt business operations, and target critical network infrastructure.
SHORT-BURST DDoS ATTACKS INCREASE BY 208%
Cloudflare’s threat intelligence team identified a 208% surge in short-duration, low-bandwidth attacks lasting less than 10 minutes and measuring below 1 Gbps. These attacks are frequently associated with booter and stresser services that allow cybercriminals to launch disruptive traffic floods with minimal technical expertise. Meanwhile, hyper-volumetric attacks exceeding 1 Tbps declined by approximately 69%, dropping from 805 incidents in the second quarter to 251 in the third quarter. The decrease may be connected to international law enforcement operations targeting major IoT botnets, including AISURU, KimWolf, JackSkid, and Mossad. However, emerging botnet variants such as Dysphoria and Evooo1Bot demonstrate that the threat continues to evolve.
DNS AMPLIFICATION ATTACKS SURGE AS HACKERS CHANGE TACTICS
Cybercriminals are also shifting their attack methods, with DNS amplification attacks increasing by 215% during the reporting period. These attacks exploit vulnerable DNS infrastructure to generate large volumes of traffic directed toward targeted networks, potentially overwhelming servers and disrupting online services. Cloudflare also observed a substantial decline in Connectionless Lightweight Directory Access Protocol (CLDAP) attacks as threat actors increasingly relied on DNS amplification and UDP flooding techniques. Media and publishing organizations, information technology companies, telecommunications providers, and software businesses were among the most frequently targeted industries. The United States ranked as the most attacked country, followed by China and Indonesia.
ORGANIZATIONS URGED TO STRENGTHEN DDoS PROTECTION
The sharp increase in DDoS activity highlights the growing importance of automated cybersecurity defenses, continuous network monitoring, and resilient infrastructure. Organizations should implement DDoS mitigation services, traffic filtering, rate limiting, and incident response procedures to reduce the risk of service disruptions. Security teams should also monitor unusual network traffic patterns, secure exposed infrastructure, and coordinate with hosting providers to identify malicious activity before it escalates. With millions of attacks occurring every quarter, Cloudflare’s findings demonstrate that businesses must prepare for both massive traffic floods and smaller, repeated attacks capable of disrupting vulnerable systems.