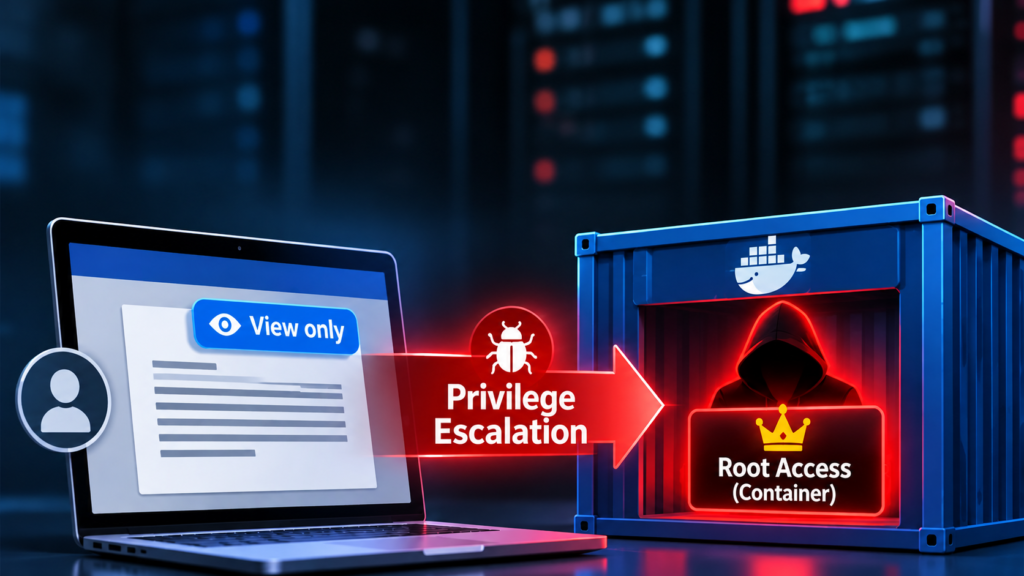
Security vulnerabilities affecting ONLYOFFICE Docs could allow attackers with view-only document access to escalate their privileges and potentially gain root-level control within an affected application container. The flaws raise concerns about access-control enforcement and the security of collaborative document environments. ONLYOFFICE Docs is widely used for online document editing, file sharing, and integration with enterprise collaboration platforms, making privilege-escalation vulnerabilities particularly concerning for organizations handling sensitive information.
Researchers identified security weaknesses that could undermine the restrictions normally imposed on users granted read-only permissions. By exploiting vulnerable application functionality, an attacker could potentially move beyond authorized document viewing and execute operations with elevated privileges inside the container hosting ONLYOFFICE Docs. Root access within a container could expose application data, configuration files, and stored credentials, depending on the deployment. However, container-level root access does not automatically provide root privileges on the underlying host operating system.
Organizations running ONLYOFFICE Docs should review vendor security advisories, identify affected deployments, and install applicable security updates. Administrators should also restrict access to document services, enforce least-privilege permissions, monitor suspicious application activity, and avoid running containers with unnecessary privileges. Additional safeguards, including container isolation, network segmentation, and credential protection, can help reduce the potential impact of exploitation.