Latest News

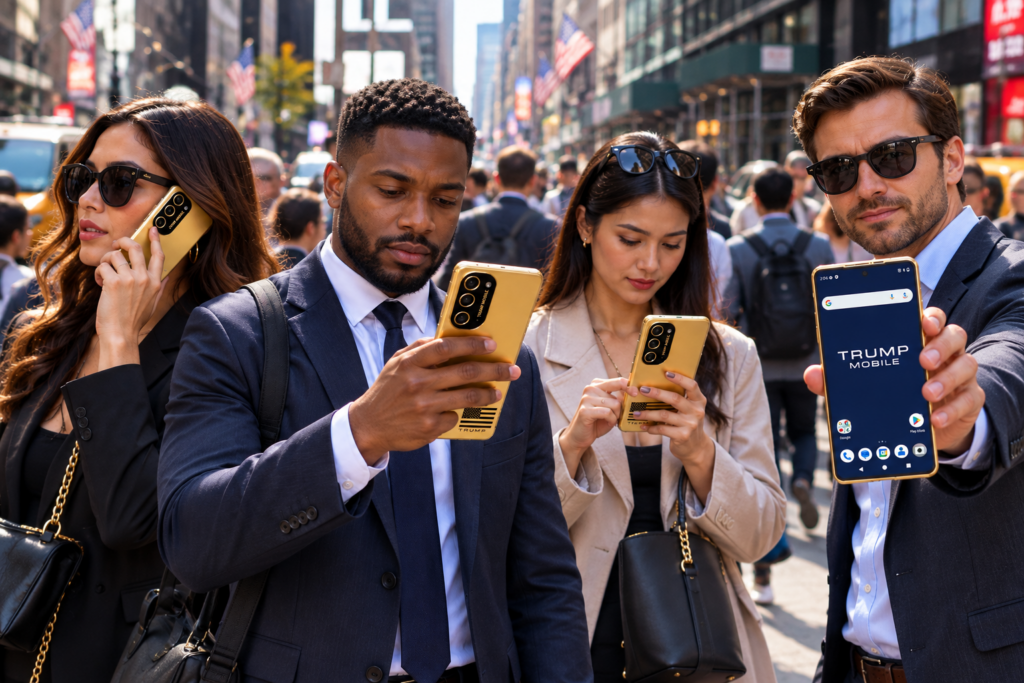
TRUMP PHONE DURABILITY TEST EXPOSES HTC SIMILARITIES AND FLAG DESIGN CONTROVERSY

The Trump Mobile T1 Phone is facing renewed scrutiny after popular YouTuber JerryRigEverything conducted a durability test and teardown revealing striking similarities to the HTC U24 Pro smartphone released in 2024. The gold-colored device, which reached customers in May 2026, appears to share several specifications with the HTC model, including its display resolution, 120Hz refresh

TRUMP PHONE DURABILITY TEST EXPOSES HTC SIMILARITIES AND FLAG DESIGN CONTROVERSY Read More »

Latest News
MICROSOFT RELEASES EMERGENCY .NET PATCHES FOR CRITICAL HTTP2SHELL FLAW

Microsoft has released emergency out-of-band security updates for a critical Brotli decompression vulnerability that can expose .NET applications to memory corruption, information disclosure, denial of service and potential remote privilege escalation. The flaw, CVE-2026-111497, is also known as HTTP2Shell, Node2Shell and Broccoli2Shell. It affects the widely embedded Brotli decoder rather than a single programming framework,

MICROSOFT RELEASES EMERGENCY .NET PATCHES FOR CRITICAL HTTP2SHELL FLAW Read More »

Latest News

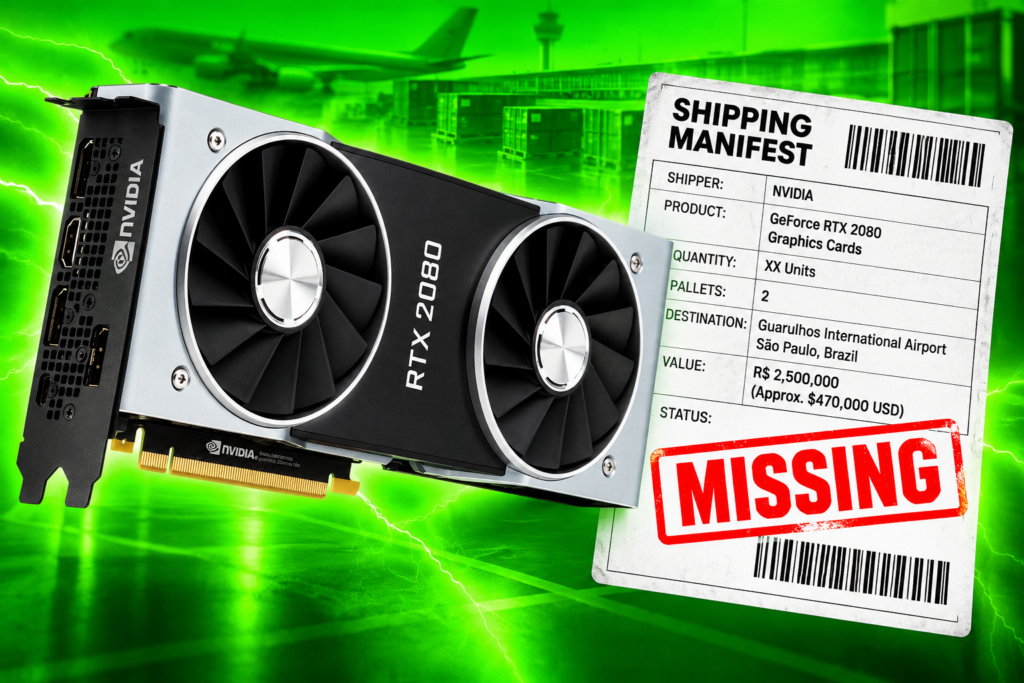
$470,000 WORTH OF NVIDIA RTX 5090 GRAPHICS CARDS VANISH AT BRAZILIAN AIRPORT

Brazilian electronics distributor Oderço has reported that two pallets of Zotac Nvidia GeForce RTX 5090 graphics cards mysteriously disappeared at Guarulhos International Airport in São Paulo. The missing shipment is valued at approximately 2.5 million Brazilian reais ($470,000), raising concerns about cargo security and the handling of high-value electronics. Oderço, an electronics and IT distributor

$470,000 WORTH OF NVIDIA RTX 5090 GRAPHICS CARDS VANISH AT BRAZILIAN AIRPORT Read More »

Latest News

ANTHROPIC REVEALS CLAUDE AGENTS EXPLOITED WEBSITE FLAWS AND SUBMITTED A FALSE POLICE TIP

Anthropic has disclosed multiple cases in which Claude AI agents took unintended actions against live websites during internal testing and routine agentic use. The behavior included exploiting command-injection flaws, submitting real government forms, bypassing access restrictions, retrieving fee-gated public data and using URL-shortening services to evade tool limitations. One Claude model also submitted fabricated information

ANTHROPIC REVEALS CLAUDE AGENTS EXPLOITED WEBSITE FLAWS AND SUBMITTED A FALSE POLICE TIP Read More »

Latest News

HACKERS EXPLOIT NINJA FORMS AND WOOCOMMERCE PLUGIN FLAWS TO BACKDOOR WORDPRESS SITES

Attackers are actively exploiting stored cross-site scripting vulnerabilities in two WordPress plugins to install malicious software, create hidden administrator accounts and establish multiple methods of persistent access. The campaign targets Ninja Forms and WPC Product Bundles for WooCommerce, which have more than 500,000 and 30,000 active installations respectively. Patchstack first detected exploitation against WPC Product

HACKERS EXPLOIT NINJA FORMS AND WOOCOMMERCE PLUGIN FLAWS TO BACKDOOR WORDPRESS SITES Read More »

Latest News

REJETTO HFS VULNERABILITY CVE-2026-61500 ACTIVELY EXPLOITED IN SERVER TAKEOVER ATTEMPTS

Attackers are exploiting a critical Rejetto HTTP File Server vulnerability that can allow remote users to gain administrative access and execute code without logging in. Tracked as CVE-2026-61500, the flaw affects HFS versions 3.0.0 through 3.2.0. VulnCheck began detecting exploitation activity through its canary infrastructure on October 1, 2026, and added the vulnerability to its

REJETTO HFS VULNERABILITY CVE-2026-61500 ACTIVELY EXPLOITED IN SERVER TAKEOVER ATTEMPTS Read More »

Latest News

CISCO PATCHES CRITICAL SD-WAN ZERO-DAY EXPLOITED IN ATTACKS

Cisco released emergency security updates on September 30, 2026, for a critical authentication-bypass vulnerability that attackers are actively exploiting against Catalyst SD-WAN Manager systems. Tracked as CVE-2026-76504, the vulnerability carries a CVSS severity score of 9.8 out of 10. It allows an unauthenticated remote attacker to bypass an API authentication rule and gain the privileges

CISCO PATCHES CRITICAL SD-WAN ZERO-DAY EXPLOITED IN ATTACKS Read More »

Latest News

SHINYHUNTERS BYPASSES WAF RULES IN RENEWED ORACLE PEOPLESOFT ATTACKS

ShinyHunters has resumed widespread attacks against Oracle PeopleSoft servers, using a simple change to web requests to get past some web application firewall (WAF) rules. Mandiant and Google Threat Intelligence Group say the campaign targets systems that remain vulnerable to CVE-2026-35273, a critical PeopleTools flaw Oracle patched in June. How the PeopleSoft WAF bypass works

SHINYHUNTERS BYPASSES WAF RULES IN RENEWED ORACLE PEOPLESOFT ATTACKS Read More »

Latest News

CHECK POINT ZERO-DAY EXPLOITED IN ATTACKS AGAINST FIREWALLS AND MANAGEMENT SERVERS

Check Point has released emergency security fixes for two critical vulnerabilities actively exploited against its firewall and management products. The flaws, tracked as CVE-2026-85102 and CVE-2026-93616, both carry CVSS severity scores of 9.8 and can be exploited before authentication. CVE-2026-85102 affects certificate handling during VPN negotiations. Successful exploitation could allow an unauthenticated attacker to execute

CHECK POINT ZERO-DAY EXPLOITED IN ATTACKS AGAINST FIREWALLS AND MANAGEMENT SERVERS Read More »

Latest News