Google released an emergency Chrome security update on November 9, 2026, addressing CVE-2026-125350, a high-severity use-after-free vulnerability in the browser’s XML component. Google confirmed that attackers are actively exploiting the flaw but has not disclosed the threat actors, affected organizations or attack methods. The vulnerability was reported anonymously on November 6, just three days before the security update. The latest Chrome release addresses nine security vulnerabilities, including several high-severity memory corruption flaws.
CHROME SECURITY UPDATE ADDRESSES NINE VULNERABILITIES
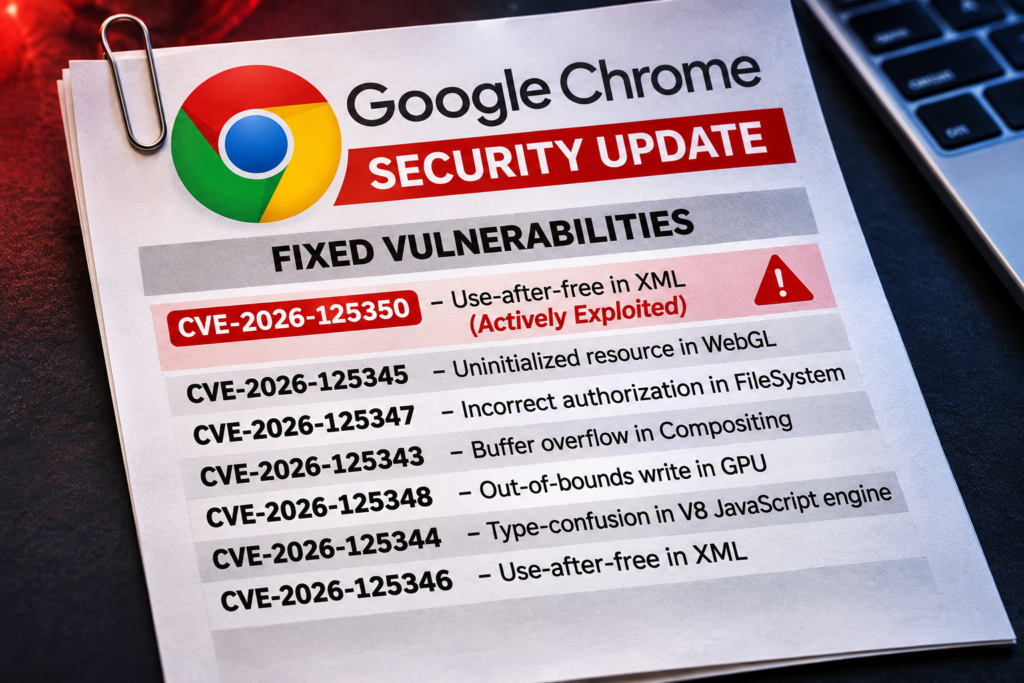
Google released patched Chrome versions 157.0.8103.50 and 157.0.8103.51 for Windows and macOS, and 157.0.8103.50 for Linux. Extended Stable users should update to version 156.0.8078.96 or later. The security fixes address the following vulnerabilities:
- CVE-2026-125350: Actively exploited use-after-free vulnerability in XML.
- CVE-2026-125345: Uninitialized resource vulnerability in WebGL.
- CVE-2026-125347: Incorrect authorization vulnerability in FileSystem.
- CVE-2026-125343: Buffer overflow vulnerability in Compositing.
- CVE-2026-125348: Out-of-bounds write vulnerability in GPU.
- CVE-2026-125344: Type-confusion vulnerability in the V8 JavaScript engine.
- CVE-2026-125346: Additional use-after-free vulnerability in XML.
Google has not confirmed active exploitation of the additional vulnerabilities. Use-after-free flaws can allow attackers to manipulate released memory, potentially causing browser crashes, memory corruption or arbitrary code execution. Technical details surrounding the confirmed zero-day remain restricted to prevent further exploitation.
ENTERPRISE DEFENDERS URGED TO DEPLOY PATCHES IMMEDIATELY
Security teams should prioritize Chrome updates across Windows, macOS and Linux endpoints, verify patched versions and require users to relaunch their browsers. Administrators should monitor endpoint telemetry for suspicious Chrome processes, unexpected downloads and unusual browser crashes that could indicate exploitation. Organizations using Microsoft Edge, Brave, Opera or other Chromium-based browsers must separately verify vendor security updates. With active exploitation confirmed, unpatched systems remain vulnerable to additional attacks as threat actors analyze publicly released patches to develop new exploits.