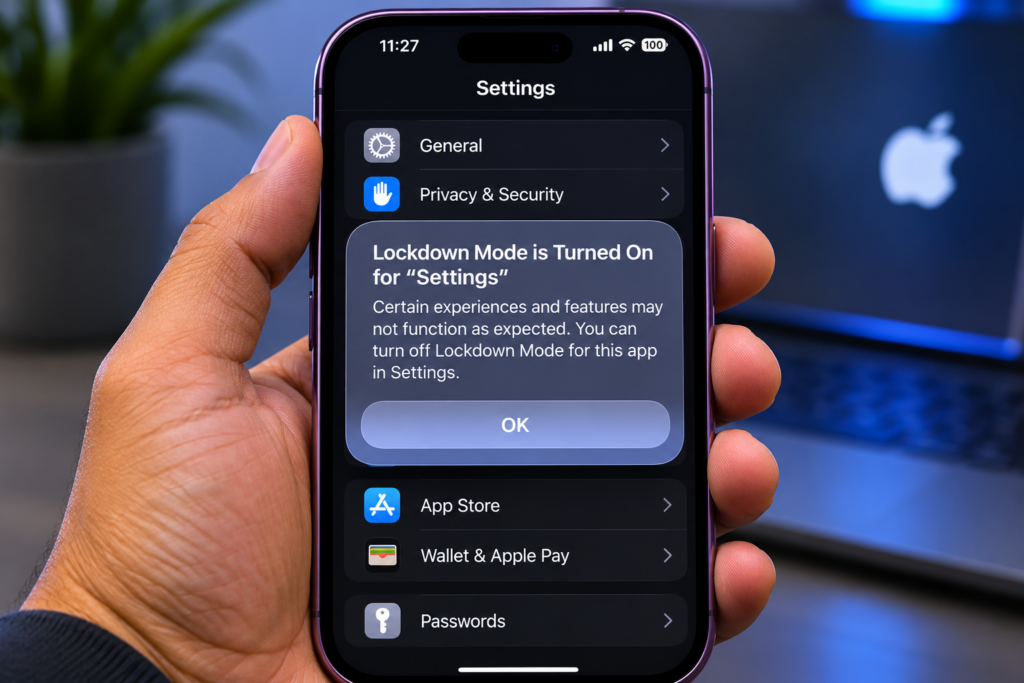
California-based security company Calif has reportedly demonstrated a successful jailbreak of an Apple iPhone with Lockdown Mode enabled, raising concerns about the effectiveness of Apple’s advanced security protections against sophisticated cyberattacks. Security researchers released a video demonstrating how a malicious PDF file delivered through Apple’s AirDrop feature could trigger a jailbreak, potentially bypassing security restrictions designed to protect high-risk users. Lockdown Mode is specifically engineered to reduce the attack surface of iPhones by limiting certain features, attachments, and communication methods commonly targeted by advanced spyware and exploit campaigns.
JAILBREAK COULD EXPOSE SENSITIVE DATA AND BANKING APPLICATIONS
The demonstrated jailbreak highlights the potential consequences of attackers gaining elevated privileges on an iPhone. Jailbreaking can allow modifications to system interfaces, installation of unauthorized software, changes to security configurations, and interference with operating system protections. Depending on the level of access achieved, a successful exploit could potentially expose sensitive information stored on the device, including personal communications, authentication credentials, and financial application data. However, a jailbreak alone does not establish that attackers can automatically access protected banking applications or bypass every security mechanism. The demonstration raises broader concerns about malicious document processing and whether sophisticated exploit chains could undermine protections intended to defend against targeted mobile attacks.
SECURITY CONCERNS PERSIST FOLLOWING IOS 27.2 UPDATE
Researchers also reportedly observed that the affected iPhone remained compromised after its operating system was updated to iOS 27.2, raising questions about the persistence of the demonstrated jailbreak and the effectiveness of software updates in restoring device security. The reported behavior warrants further technical investigation to determine whether the exploit survived the update, whether the device retained unauthorized modifications, and which vulnerabilities were involved. Apple users should continue installing official security updates, restrict unsolicited AirDrop transfers, and exercise caution when receiving unexpected files. The demonstration underscores the importance of layered mobile security, particularly for journalists, executives, government officials, and other individuals who may face sophisticated targeted attacks.